Colorado Springs, CO

Your Clarity. Your Strategy. Your Next Step.

Stand2

Security & Emergency Management Blog

Blog Image

Beware the Sandworm: Shai‑Hulud and the New Shape of Package‑Manager Worms

Beware the Sandworm: Shai‑Hulud and the New Shape of Package‑Manager WormsAaron Gilmore Published on: 2026/01/30

Shai‑Hulud and Sha1‑Hulud 2.0 show how npm worms spread via stolen tokens. Learn how to lock publishing, harden CI, and rotate secrets fast.
Covenant Health Ransomware: The Real Cost of Revised Impact

Covenant Health Ransomware: The Real Cost of Revised Impact

Covenant Health Ransomware: The Real Cost of Revised ImpactAaron Gilmore
Published on: 2026/01/28

When breach impact gets revised upward, the cost isn’t just records—it’s trust, governance, notification waves, and long-tail recovery work. Lessons from Covenant Health.

revised impact breach notification healthcare ransomware impact analysisbreach notification wavesHIPAA breach notification timelineforensic investigation scopecredit monitoring costsincident response governance
Jaguar Land Rover’s Production Disruption: Cyber Risk Becomes Supply Chain Risk

Jaguar Land Rover’s Production Disruption: Cyber Risk Becomes Supply Chain Risk

Jaguar Land Rover’s Production Disruption: Cyber Risk Becomes Supply Chain RiskAaron Gilmore
Published on: 2026/01/09

JLR’s 2025 cyber disruption shows how IT outages become supply-chain failures. Protect ERP/MES/identity, test IT/OT segmentation, and plan fallback operations.

cyber supply chain riskJaguar Land Rover cyber incidentmanufacturing cyber disruptionbusiness interruptionIT/OT segmentationoperational resiliencesupplier cyber riskC-SCRM
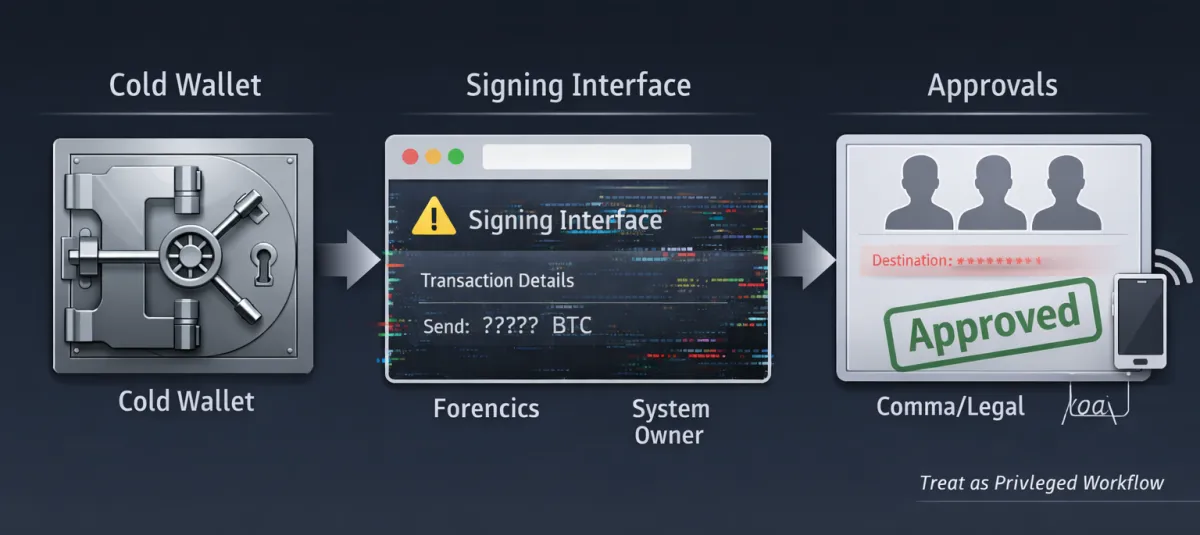
Bybit $1.5B Theft: Cold Wallet Controls Still Fail

Bybit $1.5B Theft: Cold Wallet Controls Still Fail

Bybit $1.5B Theft: Cold Wallet Controls Still FailAaron Gilmore
Published on: 2026/01/02

The Bybit theft shows “cold storage” fails when signing/approval workflows are deceived. Lessons for privileged approvals, vendor risk, and comms.

Bybit $1.5B theft cold wallet workflowSafe{Wallet} compromiseprivileged approval workflowthird-party signing interface
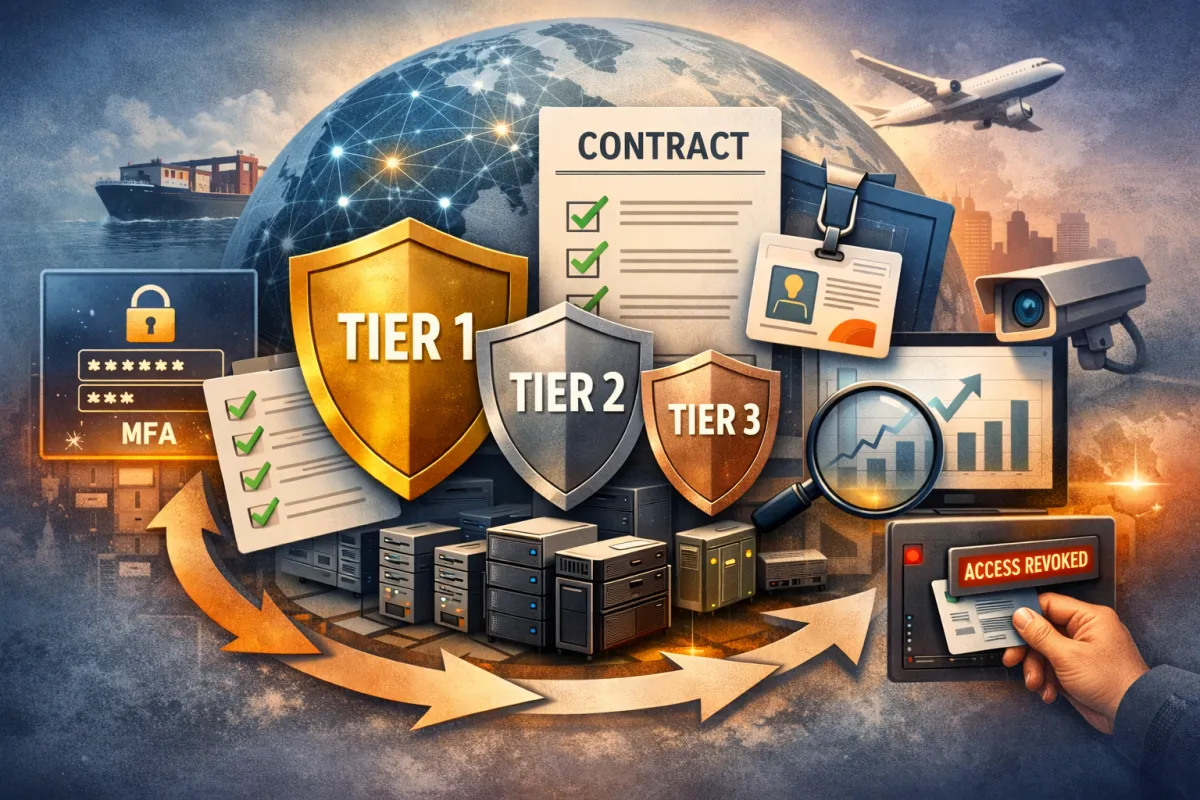
Right-Sized Third-Party Security for SMB Organizations

Right-Sized Third-Party Security for SMB Organizations

Right-Sized Third-Party Security for SMB OrganizationsAaron Gilmore
Published on: 2025/12/26

A practical vendor-risk program for SMBs: tier vendors, set minimum controls, collect lightweight evidence, and review access on a cadence—without GRC bloat.

right-sized third-party security programthird-party risk management SMBvendor risk tierssupply chain securityvendor security checklistcontract security requirementsvendor access review

About Our Content

AI tools assist with research, ideation, and content organization on this blog. All posts are reviewed and approved by our cybersecurity team before publication. Our goal is to provide accurate, actionable insights informed by real-world experience.

This content is for informational purposes only and does not constitute professional cybersecurity, legal, or compliance advice.

The right time to build clarity is now.

Connect With Me

© 2026 BEES COMPUTING. All rights reserved.

Designed & Developed by KATALYST CRM