Colorado Springs, CO

Your Clarity. Your Strategy. Your Next Step.

Stand2

Security & Emergency Management Blog

Blog Image

Beware the Sandworm: Shai‑Hulud and the New Shape of Package‑Manager Worms

Beware the Sandworm: Shai‑Hulud and the New Shape of Package‑Manager WormsAaron Gilmore Published on: 2026/01/30

Shai‑Hulud and Sha1‑Hulud 2.0 show how npm worms spread via stolen tokens. Learn how to lock publishing, harden CI, and rotate secrets fast.
Beware the Sandworm: Shai‑Hulud and the New Shape of Package‑Manager Worms

Beware the Sandworm: Shai‑Hulud and the New Shape of Package‑Manager Worms

Beware the Sandworm: Shai‑Hulud and the New Shape of Package‑Manager WormsAaron Gilmore
Published on: 2026/01/30

Shai‑Hulud and Sha1‑Hulud 2.0 show how npm worms spread via stolen tokens. Learn how to lock publishing, harden CI, and rotate secrets fast.
Shai‑Hulud npm wormpackage manager wormsoftware supply chain attacknpm supply chain compromiseCI/CD token thefttrusted publishing OIDCsecrets leakageGitHub reposdependency install scriptsSBOM and dependency inventory
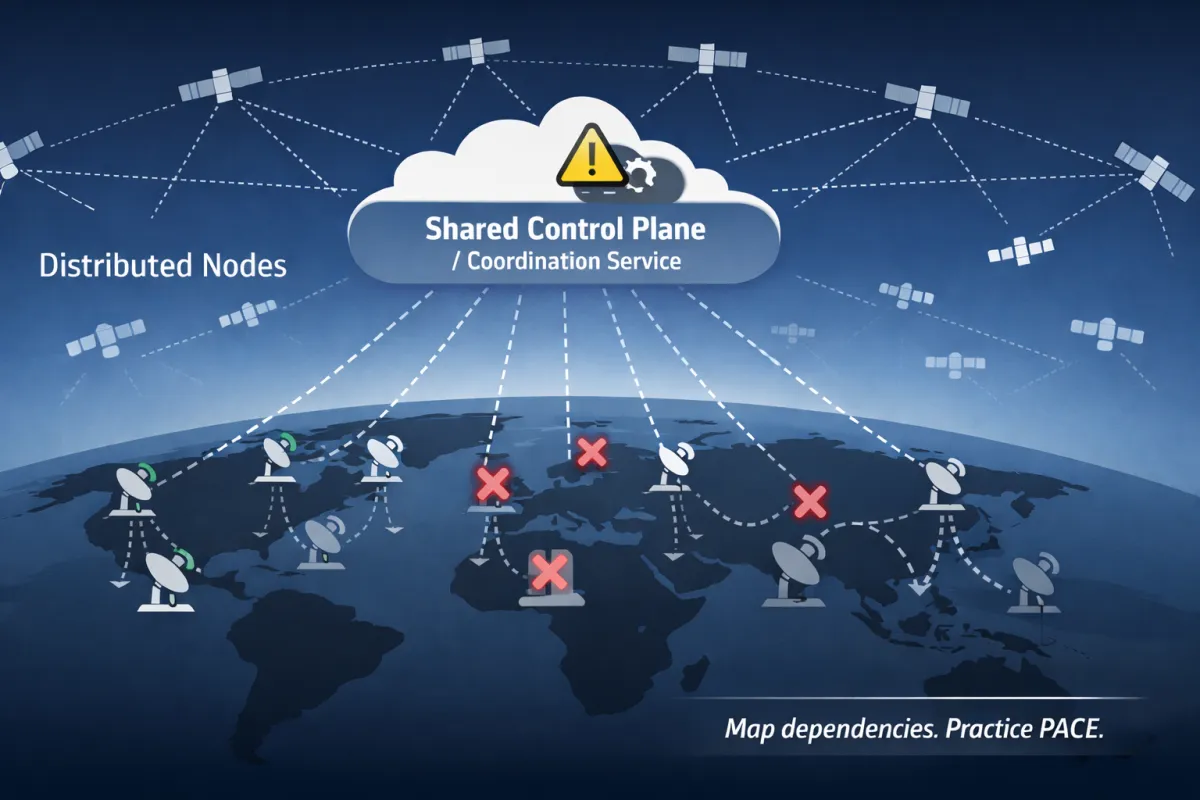
Starlink Global Outage: Single-Point Software Failures

Starlink Global Outage: Single-Point Software Failures

Starlink Global Outage: Single-Point Software FailuresAaron Gilmore
Published on: 2026/01/16

Starlink’s July 2025 outage shows “global” systems can share one weak point: the control-plane software that coordinates everything.

Starlink global outage satellite internet outagecontrol plane failuresingle point of failuredependency mappingPACE communications
Jaguar Land Rover’s Production Disruption: Cyber Risk Becomes Supply Chain Risk

Jaguar Land Rover’s Production Disruption: Cyber Risk Becomes Supply Chain Risk

Jaguar Land Rover’s Production Disruption: Cyber Risk Becomes Supply Chain RiskAaron Gilmore
Published on: 2026/01/09

JLR’s 2025 cyber disruption shows how IT outages become supply-chain failures. Protect ERP/MES/identity, test IT/OT segmentation, and plan fallback operations.

cyber supply chain riskJaguar Land Rover cyber incidentmanufacturing cyber disruptionbusiness interruptionIT/OT segmentationoperational resiliencesupplier cyber riskC-SCRM
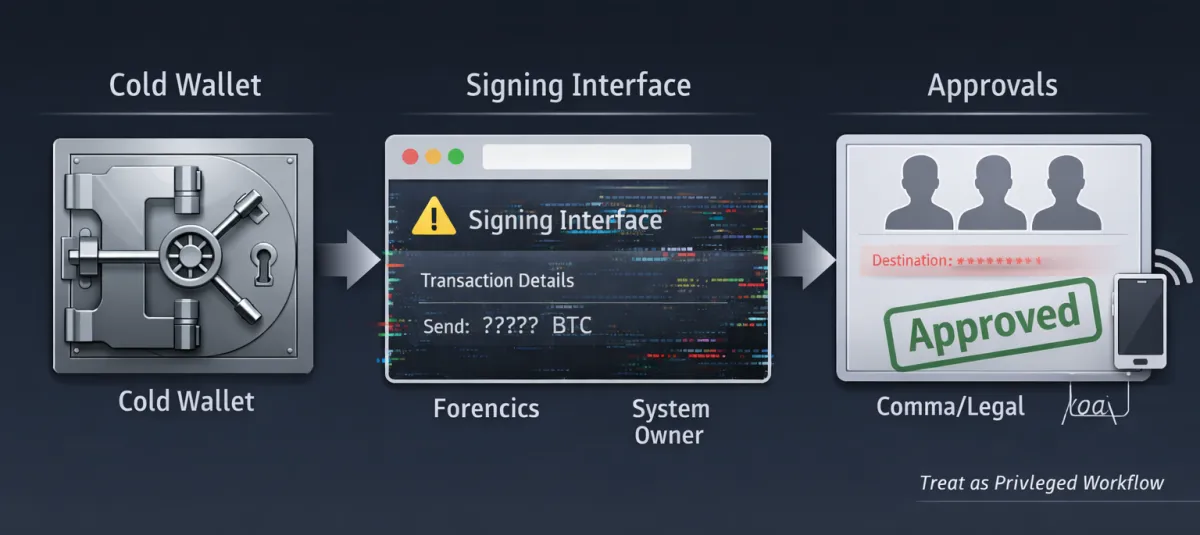
Bybit $1.5B Theft: Cold Wallet Controls Still Fail

Bybit $1.5B Theft: Cold Wallet Controls Still Fail

Bybit $1.5B Theft: Cold Wallet Controls Still FailAaron Gilmore
Published on: 2026/01/02

The Bybit theft shows “cold storage” fails when signing/approval workflows are deceived. Lessons for privileged approvals, vendor risk, and comms.

Bybit $1.5B theft cold wallet workflowSafe{Wallet} compromiseprivileged approval workflowthird-party signing interface

The right time to build clarity is now.

Get in Touch

© 2026 BEES COMPUTING. All rights reserved.

Designed & Developed by KATALYST CRM